Turn privacy governance into continuous operations.
ROPA, impact assessments and breach response that keep up with the business, not the audit calendar
assessments start from ROPA and discovery, not a blank form
breach clock tracked from first alert to Board notice
accuracy on automated privacy impact assessments.
Three modules, one governance record.
An assessment reads the record of processing. An incident reads both.
The documentation is always one quarter behind.
Every assessment starts from a blank page, answering what was already answered elsewhere.
The record changes once a year, before the audit.
The record and the reality drift apart
The next audit finds it first
Assess, record, respond, and keep it current.
Four moves, one record underneath them.
Starts from known systems and vendors
Risk scored, reviewer set automatically
Activities and transfers stay current
Incidents run through evidence trails
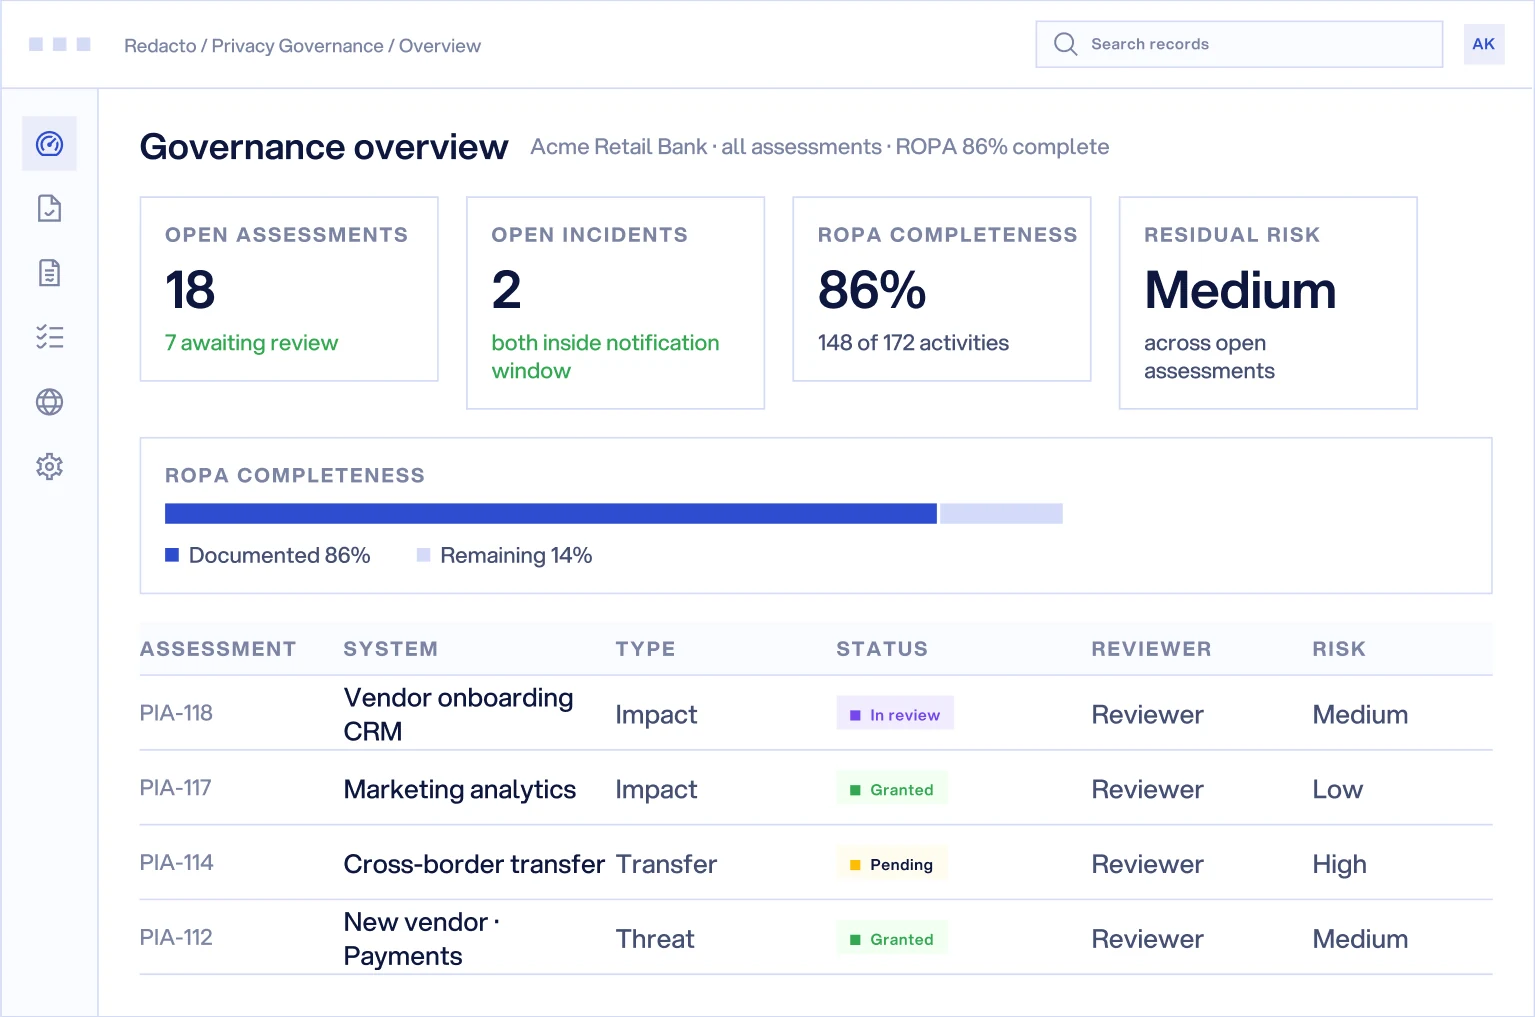
Governance that keeps its own record.
Assessment templates
Impact, transfer and threat assessments that start prefilled from connected context.
Risk scoring and review
Score responses, route what needs a human, record the decision.
Notification timers
Track the clock against the obligation, and hold the record of what was sent.
Living ROPA
Processing activities linked to the systems and vendors that actually touch them.
Breach workflow
Intake, severity, containment, notification and closure in one trail.
Audit ready evidence
Every approval, version and change with a trail behind it.
Connected to the systems the record describes.
Pull context from identity, data, procurement and vendor systems.
7,000+ integrations
A leading NBFC cut the time to complete a privacy impact assessment from weeks to days.
Read the guideper assessment
What privacy teams ask before the demo.
Can we bring our existing assessment template?
Yes. Templates are configurable, rebuilt question for question, then prefilled from the connected record.
How is a record of processing kept current after the first build?
The record is linked to the systems and vendors it describes, so a change in either raises a task to update the activity, and every edit keeps its earlier version.
Does the breach workflow track notification deadlines?
Yes. Each incident carries a notification clock against the obligation, and every notice sent is held in the incident record.
Who can see an assessment while it is still in progress?
Access follows role. Assessors and reviewers on the assessment see it, and everyone else sees only what their role allows.
See Privacy Governance against your own assessments
Thirty minutes. Bring one assessment you run today.
Tell us where to send the invite. The message is optional.