Every choice honoured.
Every request answered.
Capture consent where it happens, honour it everywhere it matters, and answer every Data Principal request on the clock.
integrations, every choice carried
and ISO 27001 certified, IAB Europe TCF Registered CMP, with audit logging on every consent event.
per Data Principal, on web, app, phone or paper.
Three products built around the Data Principal.
Consent Management captures and proves the choice. Cookie Consent does the same on your websites. DSAR & Grievance answers the person who made it.
Consent breaks quietly.
A pop-up records a choice. The systems that use the data never hear about it.
Collected in one place, ignored in another
No proof when the Board asks
Requests arrive faster than anyone can answer
From the first notice to the closed request.
Four stages. Nothing lost between them.
Notices live in every channel and language.
Every choice pushed to the systems that act on it.
Requests verified and routed to the right owner.
A timestamped record of every choice and closure.
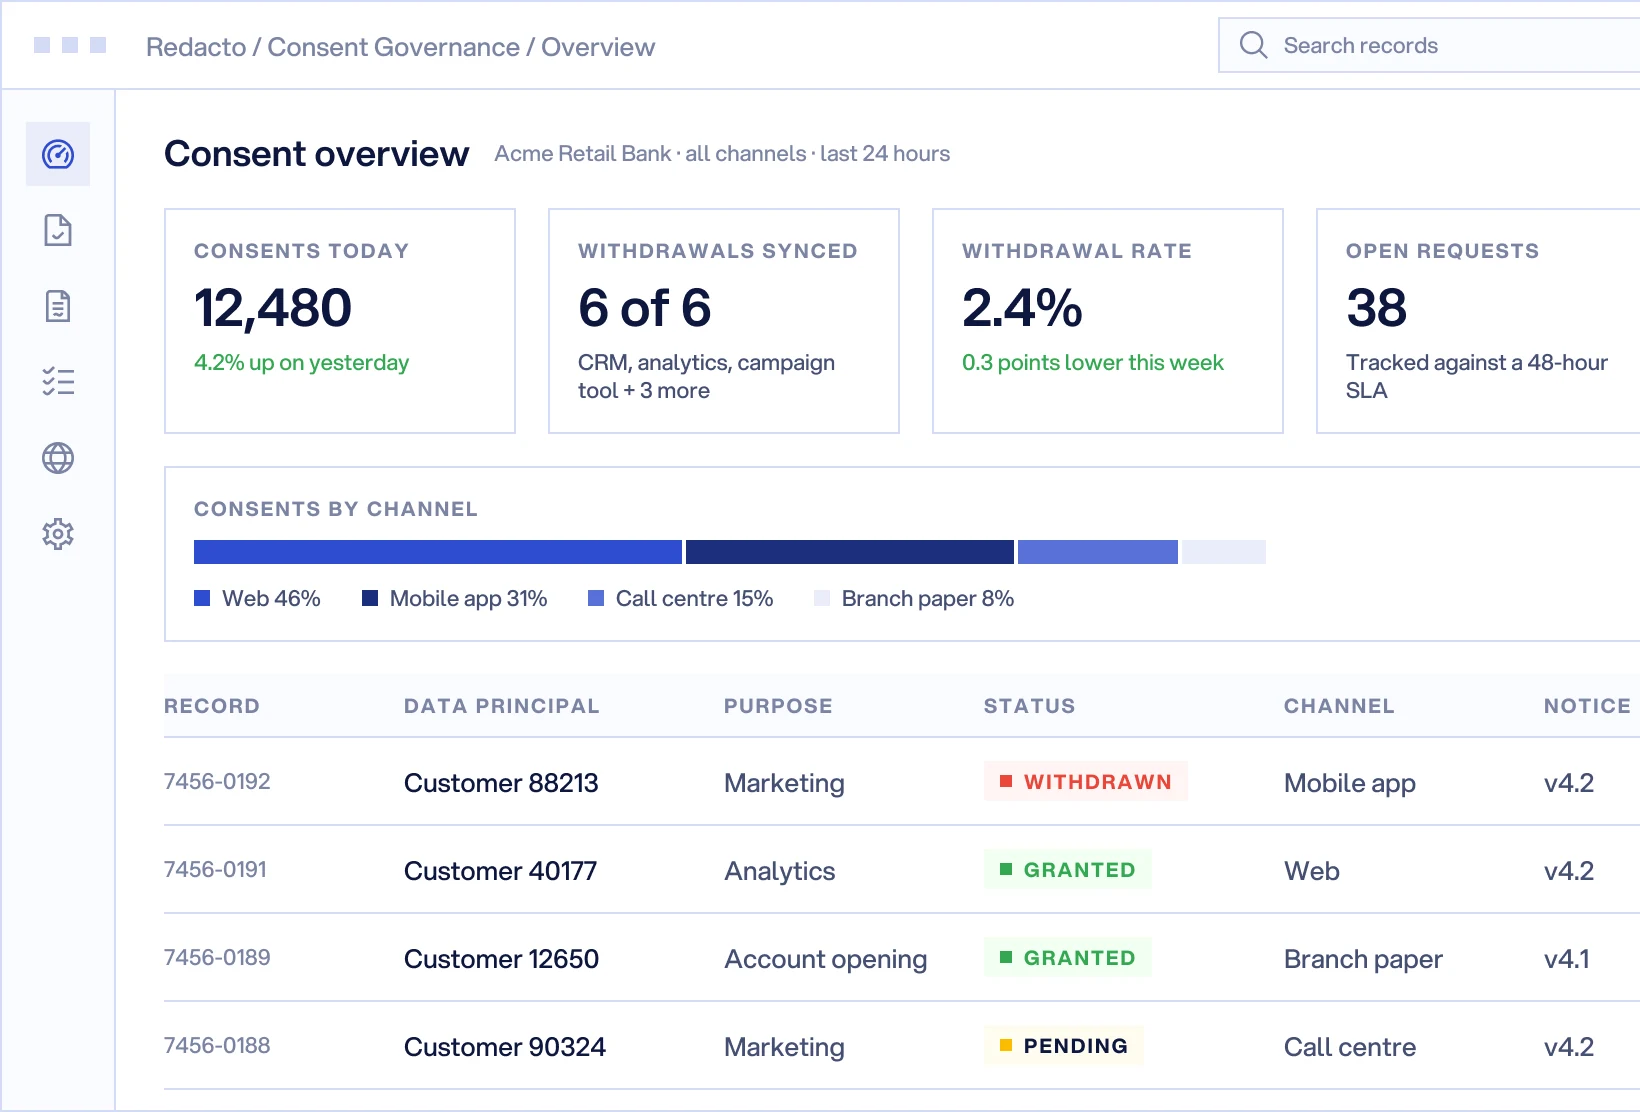
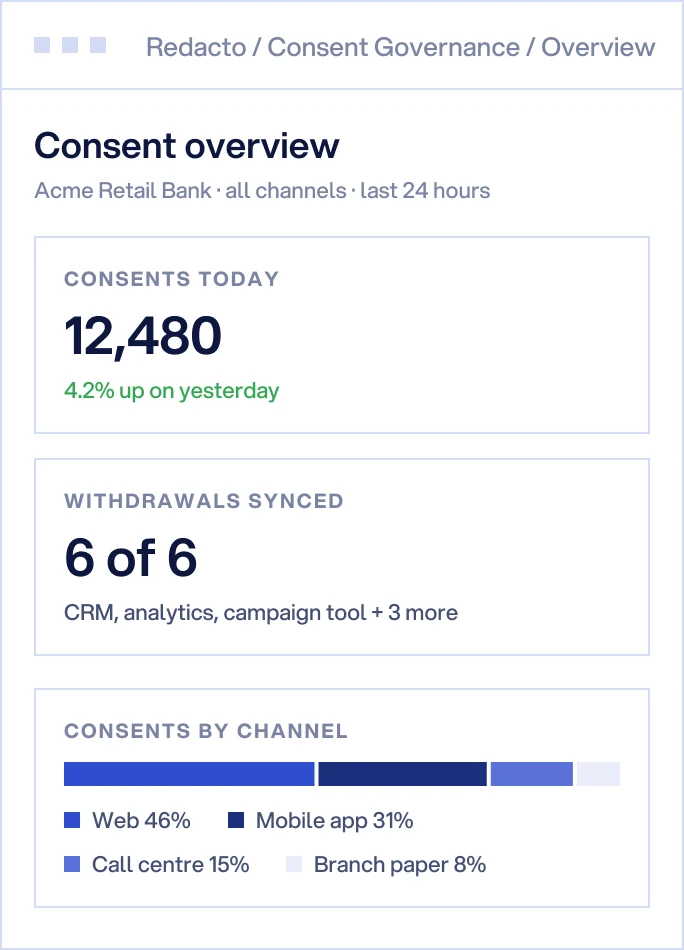
Built for the way consent actually moves.
Notice and preference centre
Branded, versioned, and published across every channel you collect on.
Multi-language notices
Serve the notice in the language the Data Principal chose, on record.
Downstream enforcement
Connect consent to the systems that use the data, so a withdrawal is acted on and not filed.
Consent Manager readiness
Structured to work with the DPDPA Consent Manager model.
Request intake and workflow
One intake route, identity verification, a clock everyone can see.
Grievance handling
Log, escalate and close grievances inside the response times the law expects.
Connected to where choices are made and used.
Collect through web, apps and call centre tooling. Enforce through CRM, marketing and analytics.
7,000+ integrations
A top public sector bank moved consent capture from six channels onto a single record.
Read the guidechannels, one record
What teams ask first.
Do the three products work together, or can we buy them separately?
Both. Each product runs on its own. Used together, they share one record, so a withdrawal or erasure request sees everything about the person.
How do you handle access, correction and erasure requests?
Every request lands in one queue. Redacto verifies the requester, finds their data across connected systems and drafts the response. An owner approves it before it goes out.
How do you keep grievances inside DPDP timelines?
Each grievance starts a clock the moment it is logged. Reminders and escalations fire before time runs out, and the full trail is kept in case the Board asks.
Does cookie consent sit on the same record as everything else?
Yes. Redacto scans your websites, sorts every cookie and blocks non-essential ones until the visitor agrees. Each choice joins the same record as web, app, call centre and branch consent.
How does enforcement reach a system with no API?
Redacto raises a task for the team that owns the system, with the choice attached, and records when it is done. The change is tracked to closure even without an integration.
Does it work with Consent Managers registered with the Data Protection Board?
Yes. A choice relayed by a registered Consent Manager lands on the same record as every other channel and is enforced and reconciled the same way.
Can a nominee act on behalf of a Data Principal?
Yes. The nominee’s request is checked against the nomination on record, then handled like any other request, on the same clock.
See magic against your own consent flows
Thirty minutes. Bring one channel you collect on today.
Tell us where to send the invite. The message is optional.