Manage third-party risk. Share trust at scale.
Enterprise risk, assessed with the context you already hold. Answer inbound security questions once instead of every time.
faster vendor assessments. Reviews start from context the platform already holds.
integrations across procurement, ticketing and document stores.
successful implementations.
Four products, one view of enterprise risk.
Vendor Risk Management looks outward and Trust Center answers your own customers. GRC & ERM keeps one risk register, and Privacy & Security Training keeps your people ready.
Third party risk runs on chasing.
Every review restarts from a blank questionnaire, every rating goes stale after onboarding, and every customer question lands on the same security team.
The questionnaire arrives empty
Risk is assessed once and never revisited
Your own customers are asking too
From first request to renewal, and back the other way.
Four stages that loop.
One place, context captured up front.
Reviewed against what's already known.
Rating updates as evidence changes.
Trust centre answers before you're asked.
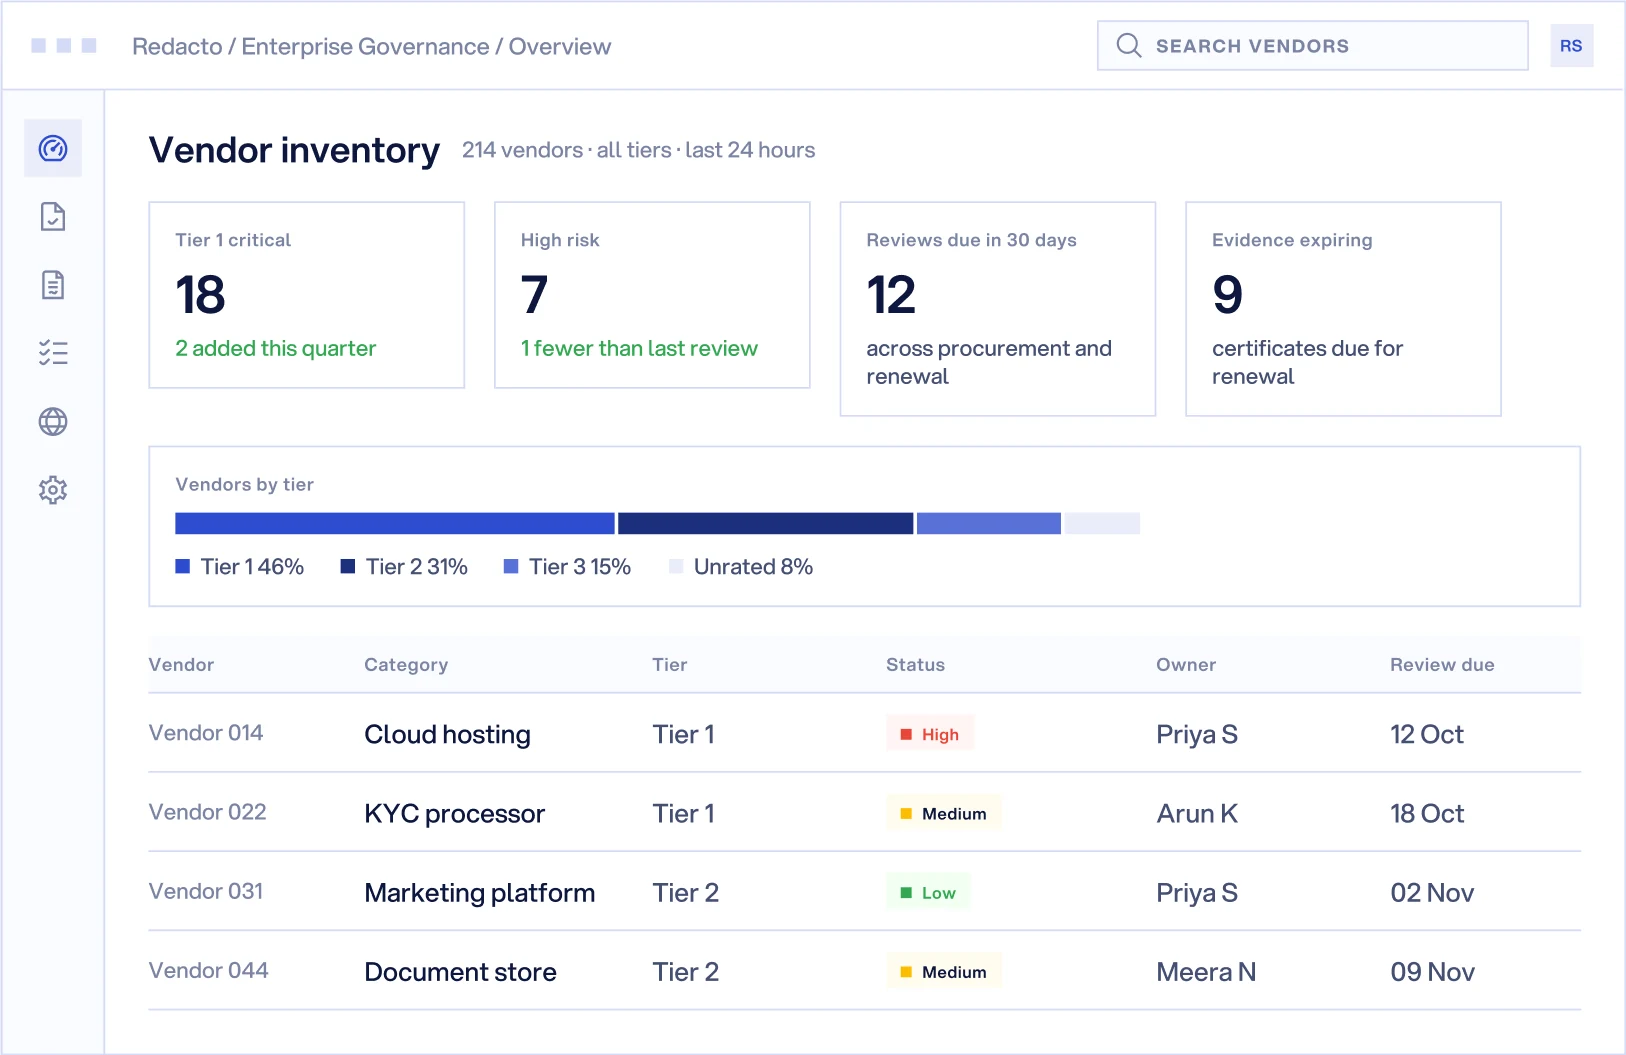
Assessment with context, and answers on tap.
Six capabilities, one record per vendor. Each one feeds the rating, and the rating feeds the next review.
Vendor intake and triage
One route in, with business context and data categories captured at the start.
Context aware assessment
The review starts from the processing activities and data the vendor actually touches.
Evidence library
Certificates, reports and policies held once and reused across every review.
Continuous risk rating
Ratings that move when the contract, the data or the evidence changes.
Trust Center
A public page that answers common security and privacy questions in your approved language.
Questionnaire automation
Draft answers to inbound questionnaires from evidence you already hold.
Connected to procurement, contracts and the deal desk.
Take intake from procurement and ticketing, read evidence from contract stores.
7,000+ integrations
A top five private bank made vendor assessments five times faster without adding headcount.
Read the guideVendor reviews start from context the platform already holds, not a blank form.
What security and procurement teams ask first.
Can the trust centre use our own approved wording?
Yes. Every published answer comes from your own library, with an owner and a review date.
Do vendors need a Redacto account to respond?
No. Vendors answer through a secure link to their own questionnaire, and their answers and evidence land on that vendor's record.
How does a risk rating change after onboarding?
It is recalculated when a contract changes, a new data category is added or a piece of evidence expires, so the rating reflects the vendor as they are now.
Can we import the questionnaires we already use?
Yes. Standard and custom questionnaires come in and are mapped to the same risk domains, so past answers stay comparable.
See Enterprise Governance against your own vendor list
Thirty minutes. Pick three vendors you reviewed this year.
Tell us where to send the invite. The message is optional.