7 best DPO-as-a-service firms for DPDP compliance in 2026


If you’re considering an external DPO before the DPDP deadline on 13 May 2027, start with two questions. Do you need one, and how do you compare the available firms?
You only need to appoint a DPO once the government classifies you as a Significant Data Fiduciary. Until then, you must still respond to people asking what data you hold about them and report breaches to the Data Protection Board. Someone in your company needs to own that work now, whether or not they hold the DPO title.
The seven firms I compared all promise expert DPO support for less than the cost of a full-time hire. That claim alone will not help you choose. The real differences are who becomes your DPO, whether the firm does the work or only advises your team, and whether breach response is included.
For each firm, I’ve covered those points, highlighted what is missing, and listed the questions to ask before signing. I’ve also included Redacto because any DPO you hire will need one place to keep the records your board or the Data Protection Board may request.
Best DPO-as-a-service firms at a glance
- Pricoris: An embedded privacy team for startups facing buyer diligence.
- Privacyglobal: One team covering DPDP and eight foreign privacy laws.
- Miniorange: A DPO and compliance platform from one provider.
- Tsaaro: Lawyers and security specialists working on one DPO team.
- Valuementor: Holds the formal DPO role and communicates with regulators.
- Sirius Star: A named officer for mid-sized firms starting from scratch.
- DPO-India: A certified team for data moving between India, the EU, and the US.
How I evaluated each DPO-as-a-service firm
I compared all seven firms using six questions you should ask before signing a DPO contract. When a firm does not answer one clearly, I’ve highlighted it in that firm’s section.
1. Who your DPO actually is
If you become a Significant Data Fiduciary, Section 10 of the DPDP Act requires an individual based in India who reports to your board. I checked whether each firm names that person or describes only a broader team.
2. Whether they do the work or only advise
Some firms answer rights requests and review vendors each month. Others design the process and leave your team to run it. I looked at where each firm falls between those two approaches.
3. Breach readiness under the DPDP Act
Section 8(6) requires notices to the Data Protection Board and every affected Data Principal. I checked whether breach response is included, which service level covers it, and whether the process follows DPDP requirements or another law’s timeline.
4. The proof you keep
Your board or a regulator may ask for records, not advice. I looked at what each firm leaves behind, including audit files, records of processing activities, DPIA records, request logs, and the systems used to store them.
5. Which laws they cover
A DPDP-only team may suit an India-only business. If you also handle EU, UK or US data, you may need one firm that can cover those laws under the same contract.
6. Published credentials and client work
I gave more weight to named qualifications such as CIPP, CIPM, DCPP and ISO 27701, along with real client examples, than to broad claims about experience.
The 7 Best DPO-as-a-Service Firms in 2026
1. Pricoris
Pricoris may suit you if you want a privacy team that already understands your business when a question arises. You hire the team on an ongoing contract, and it works like part of your company rather than an adviser you contact occasionally.
When a customer asks how you handle data, a vendor contract needs reviewing, or an incident needs coordinating, you don't have to explain your systems from scratch. The team can respond immediately.
Its work includes:
- Setting privacy responsibilities and keeping records that show ownership
- Writing and updating privacy policies and notices
- Running DPIAs for risky processing, new products and new vendors
- Training your teams
- Answering privacy questions from your legal, product, business and technology teams
- Acting as the contact for Data Principals and dealing with the Data Protection Board when required
You can use Pricoris as your external privacy contact, to support an existing team, or to oversee your wider privacy program.
I would confirm two points early.
Who is your DPO? The firm promises a qualified DPO but does not name anyone. If you are a Significant Data Fiduciary, the person must be based in India and report to your board.
How are breach notices handled? Pricoris coordinates incidents, but you should ask how it sends Section 8(6) notices to the Data Protection Board and affected Data Principals.
Why Pricoris is better for startups facing enterprise diligence or fundraising
When an enterprise buyer or investor asks who owns privacy in your company, a name on your website will not be enough. They may want evidence that vendor contracts are reviewed, DPIAs happen before launches, and Data Principal requests receive consistent responses.
Pricoris builds that work into your business and keeps it running. You can show buyers and investors an active privacy process instead of a policy written just before the deal. If you already have legal or compliance staff, Pricoris can support them rather than replace them.
Pros
- Provides an ongoing team that learns your business.
- Runs DPIAs for new products and vendors.
- Can communicate with the Data Protection Board.
- Works alongside an existing legal team.
Cons
- No named DPO or individual credentials are published.
- The breach notification process is not explained.
- Only the DPDP Act is mentioned.
Best for
You are a startup preparing for an enterprise deal or funding round, and buyers or investors are asking who owns privacy. It also suits legal or compliance teams that need privacy expertise without hiring a full-time specialist.
2. Privacyglobal
Privacyglobal provides an outsourced DPO team under contract, allowing you to get ongoing privacy support without adding a full-time officer to payroll.
The work begins with an assessment of your current position and a privacy roadmap. The team then helps implement policies, vendor controls, and consent management, then monitors compliance and reports to your board.
Its day-to-day work includes DPIAs, data processing agreement reviews, breach notification steps, and communication with regulators.
Before signing, ask who your named DPO will be and what privacy experience they have. Privacyglobal lists ISO 27701, ISO 27001, and SOC 2 certifications, but these apply to the company, not individual DPOs.
If you are a Significant Data Fiduciary, your DPO must be an individual based in India who reports to your board. Get that confirmed in writing.
Why Privacyglobal is better for companies under several privacy laws
If your customers or teams operate outside India, the DPDP Act may not be your only obligation. Privacyglobal covers the DPDP Act, EU GDPR, UK GDPR, CCPA/CPRA, PIPEDA, PDPL, APPI, PIPL, and LGPD under one contract.
For cross-border transfers, the team maps where your data moves, identifies the rules that apply to each flow, and recommends safeguards.
You can also test the team through a short project before choosing a retainer. Options include audits, readiness checks, product launch reviews, due diligence, and M&A reviews.
Pros
- Covers DPDP and eight foreign privacy laws.
- Accepts short projects, including M&A due diligence.
- Handles breach notification and regulator communication.
- Reviews vendor risk and data processing agreements.
Cons
- No named India-based DPO is published.
- Listed certifications belong to the firm, not its DPOs.
- Its FAQ overstates which companies must appoint a DPO.
Best for
You operate in several countries and want one outsourced team covering Indian and foreign privacy laws. It also suits companies that want to begin with a one-off project before committing to a long-term DPO arrangement.
3. Miniorange
Miniorange provides a dedicated DPO for DPDP Act compliance through a virtual, outsourced, or fractional arrangement. The DPO works inside Miniorange’s own compliance platform, so the service combines the person and the software.
Your DPO handles:
- Data Principal requests for access, correction, erasure, and nomination
- Grievances, DPIAs, consent records, and records of processing activities
- Vendor onboarding and DPA renewals
- Breach response, including Data Protection Board notices
- Board reports and recurring DPDP awareness sessions
Before signing, ask three questions:
- Who will your DPO be, and what qualifications do they hold?
- How long will setup take before the DPO takes over?
- Can the DPO work in your current compliance tool, and can you export your records if you change providers?
Why Miniorange is better for getting a DPO and compliance software together
Many DPO retainers end with advice, leaving your team to carry out the work. Miniorange runs rights requests and grievances through workflows with service levels and audit trails, so execution does not fall back on your team.
Because the DPO and platform come from one provider, there is less distance between decisions and records. During a breach, the DPO sending notices to the Data Protection Board also keeps the incident file in the same system.
Pros
- Combines a DPO and compliance platform.
- Handles rights requests and grievances.
- Includes Data Protection Board notices in breach response.
- Provides recurring DPDP awareness training.
Cons
- No DPO names or credentials are published.
- No setup timeline is given.
- Covers only the DPDP Act.
Best for
You are an Indian company with DPDP-only obligations and no compliance platform. If you already use a privacy tool, confirm that the DPO can work within it before signing.
4. Tsaaro
Tsaaro’s DPO team includes privacy lawyers, information security specialists, and compliance engineers. That mix helps when one problem, such as a breach, requires both a legal response and a security fix.
The work begins with a gap assessment. The team inventories your personal data, maps how it moves between systems and third parties, and identifies high-risk processing. You receive a report with a prioritized list of fixes.
The team then:
- Drafts privacy notices, retention schedules, DPAs, records of processing activities and DPIA templates
- Builds consent and rights workflows, including nomination requests
- Trains leadership and HR, marketing, product and IT teams
- Runs monthly health checks, quarterly audits and an annual review
- Provides 24/7 breach response from initial triage through regulator notification
Before signing, confirm who will act as your named DPO if you become a Significant Data Fiduciary. A team model still needs one India-based individual reporting to your board.
Also ask which checks and audits are included in the base contract and which platform powers the reporting dashboard.
Why Tsaaro is better when privacy work also needs security expertise
A breach is both a legal and security problem. Tsaaro is CERT-In impaneled and certified to ISO 27001 and ISO 27701. Its security specialists work alongside privacy lawyers on the same DPO team.
During an incident, one team handles triage, containment advice, and regulator notices, reducing the need to coordinate separate firms.
The team covers the DPDP Act, EU and UK GDPR, US state laws including CCPA/CPRA, and UAE PDPL. Companies operating across these regions can use one coordinated service.
Pros
- Combines privacy lawyers and security specialists.
- Provides 24/7 breach response through regulator notification.
- Covers DPDP, GDPR, US state laws, and UAE PDPL.
- Provides role-based training for leadership and functional teams.
Cons
- No named individual DPO is published.
- The audits included in the base contract are unclear.
- The reporting platform is not named.
Best for
You run a fintech, healthcare, edtech, or AI company where a privacy incident can also become a security incident. It also suits platforms handling children’s data or operating across India, Europe, the US, or the UAE.
5. Valuementor
You can appoint Valuementor as your formal virtual DPO, allowing the team to communicate with regulators on your behalf.
A project management office runs the engagement. It begins by assessing your privacy position and regulatory scope before setting roles, reporting lines, and a roadmap.
The team then handles DPIAs, notices, consent records, records of processing activities, policies, and vendor risk reviews. Ongoing work includes compliance reports, periodic audits, and tracking regulatory changes.
Before signing, confirm three points.
Who is your named DPO, and are they based in India? A Significant Data Fiduciary requires an India-based individual who reports to its board.
Is the breach process built for DPDP? The published incident response material refers to PDPL. Ask for a process covering Section 8(6) notices to the Data Protection Board and every affected Data Principal.
What does “on-request” support mean during a breach? Get response times in writing and confirm whether the Secusy GRC platform is included.
Why Valuementor is better when you want an outside firm to hold the DPO title
Some companies want an outside provider to take the formal DPO role rather than advise an internal employee. Valuementor accepts that appointment and communicates with regulators, giving you an external regulatory contact.
If you are also working towards ISO 27701, the same team supports it alongside GDPR and the DPDP Act. Your certification and privacy work can follow one plan.
The team also tests incident response processes, not just writing them.
Pros
- Can serve as your formally appointed DPO.
- Handles communication with regulators.
- Covers DPDP, GDPR and ISO 27701 together.
- Tests incident response processes.
Cons
- No named India-based DPO is published.
- Incident response material refers to PDPL rather than DPDP.
- Response times for “on-request” support are unclear.
Best for
You are a small or mid-sized company that wants an outside provider to hold the DPO title and communicate with regulators. It also suits teams working towards ISO 27701 alongside DPDP or GDPR compliance.
6. Sirius Star
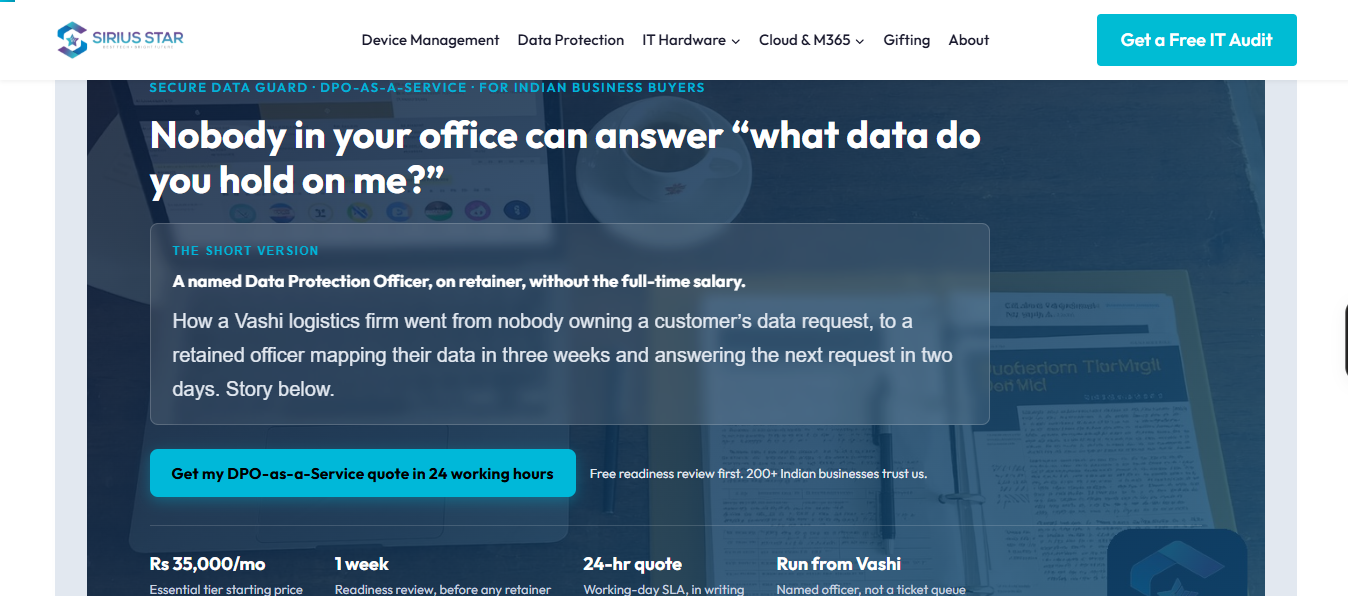
Sirius Star assigns a named officer from its Navi Mumbai team to handle your DPO duties. You work with one person instead of a ticket queue.
The officer becomes your published privacy contact, answers Data Principals and communicates with the Data Protection Board, with your approval required for serious matters.
You begin with a free one-week readiness review. It identifies the data you hold and the first three gaps to fix. During the first month, the officer builds your data map and drafts consent notices.
The officer then records and answers rights requests within the legal deadline. Every quarter, you receive an updated audit file and a plain-language leadership brief.
The scope depends on company size:
- Up to 50 employees includes a data map, privacy policy, rights requests, and quarterly file.
- Between 50 and 250 employees adds vendor reviews, contract reviews, and quarterly board briefings.
- The Significant Fiduciary tier for BFSI and pharmaceutical companies adds statutory officer duties, breach response, and Board liaison.
Before signing, ask:
- Is breach response included in the smaller plans? Section 8(6) applies to every Data Fiduciary, but this service appears only in the top tier.
- Who is your assigned officer, and what qualifications do they hold?
- Is GDPR support available if you need it?
Why Sirius Star is better for mid-sized Indian companies starting from scratch
If nobody currently owns data requests in your company, you need someone to run the role, not just advise. The Sirius Star officer builds the data map, answers requests, and maintains the audit file.
One Vashi logistics company moved from having no owner for customer data requests to completing a data map within three weeks. It answered its next request in two days.
The free review also lets you see what the officer finds before committing. With full compliance due on 13 May 2027, you still have time to fix the gaps.
Pros
- Gives you a named officer instead of a ticket queue.
- Includes a free one-week readiness review.
- The officer handles rights requests directly.
- Provides quarterly audit files and leadership briefs.
Cons
- Breach response is listed only in the top tier.
- No officer names or qualifications are published.
- Only one client example is available.
Best for
You run a mid-sized Indian business with up to 250 employees, nobody currently owns privacy, and you want one person to set up and run the work. BFSI and pharmaceutical companies expecting Significant Data Fiduciary status can consider the top tier.
7. DPO-India
An outside DPO can challenge how your product and marketing teams use personal data without reporting to them. DPO-India builds its service around that independence.
You receive support from certified privacy professionals with CIPP, CIPM, and DCPP qualifications, along with lawyers who act as your contact for regulators and Data Principals. They also raise data risks with your leadership.
What you receive depends on the scope you choose. The entry package focuses on diagnosis and documentation. It includes a half-day remote risk workshop, a prioritized plan, privacy templates, and guidance on adapting them.
Your team remains responsible for implementation, while training is limited to course recommendations.
Under the fuller scope, the DPO handles legal and setup work such as:
- Checking the lawful basis for processing under the DPDP Act, GDPR, CCPA or APPI
- Mapping sector rules to your operations
- Drafting DPAs, controller-processor contracts and data-sharing agreements
- Building processes for access, erasure and consent withdrawal requests
- Recommending security controls for each stage of the data lifecycle
- Leading breach response, assessing impact, advising on notification and documenting the incident
The service is built around GDPR, and its breach protocols follow the GDPR 72-hour reporting timeline. It also covers the DPDP Act and DPDP Rules 2025.
If India is your main exposure, confirm three points:
- The breach process includes Section 8(6) notices to the Data Protection Board and every affected Data Principal.
- Your DPO handles rights requests each month, not just setting up the process.
- Significant Data Fiduciaries receive a named India-based individual who reports to the board.
Why DPO-India is better for companies with users in India and abroad
When data collected in India moves to teams or servers in Europe or the US, one flow may fall under several laws. DPO-India reviews it against the DPDP Act, GDPR, UK GDPR, CCPA/CPRA, HIPAA, and LGPD together.
For data leaving India, the team advises on transfer methods such as standard contractual clauses, binding corporate rules, and adequacy decisions. It also covers the EU AI Act for companies developing AI products.
Pros
- Team members hold CIPP, CIPM, and DCPP qualifications.
- Covers more than 100 jurisdictions and the EU AI Act.
- Advises on SCCs, BCRs and other transfer methods.
- Leads and documents breach response.
Cons
- The entry package relies heavily on templates and advice.
- Breach protocols follow GDPR’s 72-hour timeline.
- No named individual DPO is published.
Best for
You run an AI, healthcare, or SaaS company serving users in several countries and need support across GDPR, DPDP, and cross-border transfers. If you need the DPO to run rights requests each month, confirm that responsibility before signing.
Where Redacto fits: the system your DPO works in
Every provider on this list, along with any DPO you hire internally, depends on records your teams maintain. Redacto puts those records in one place.
It is a DPDP-first platform used in production by BFSI and fintech companies. Your DPO can log in and review the work directly instead of chasing teams through emails and spreadsheets.
Day one: a data map your DPO can rely on
An outsourced DPO begins without knowing your systems. Redacto provides a starting point by:
- Scanning databases, applications, and cloud storage to list each source
- Classifying personal, health, and financial data
- Tracing where each type of data moves
- Monitoring changes so the map remains current after the first review
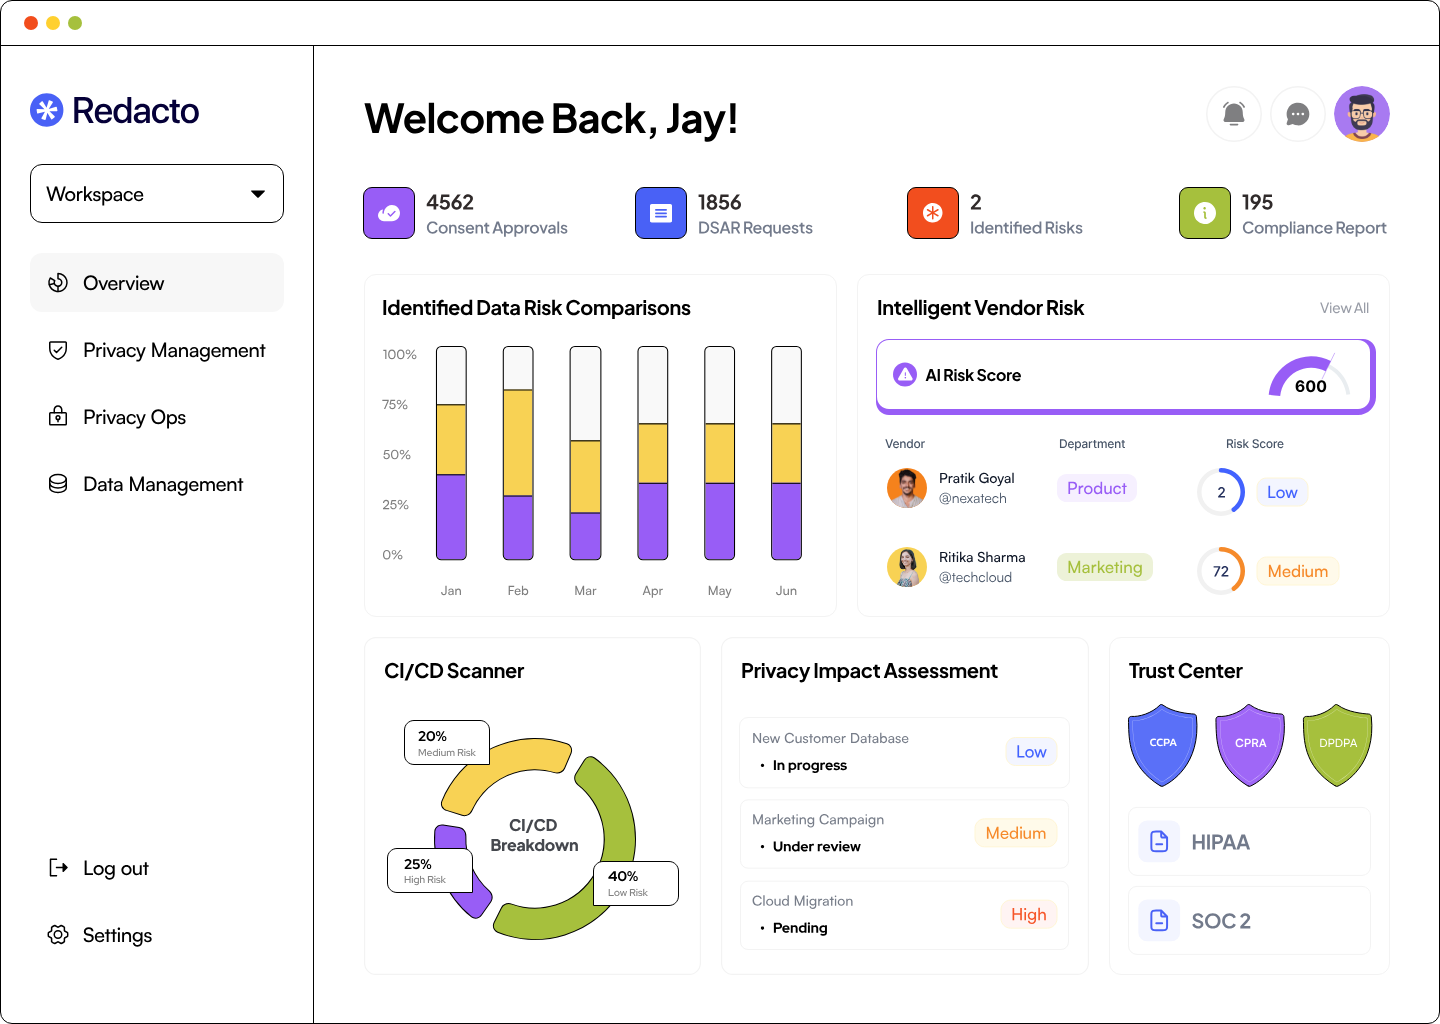
Every month brings consent, requests, and reviews into one view
Consent: Your DPO can see which consent supports each processing purpose.
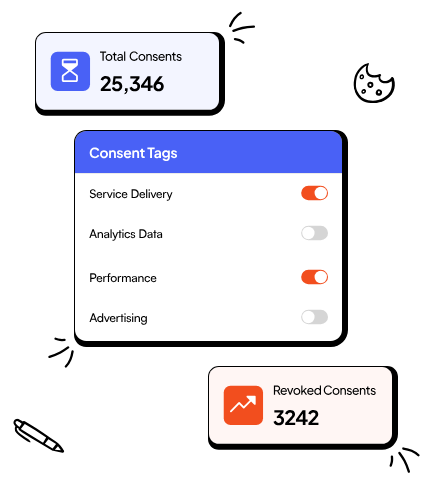
Redacto records every version of a notice and every consent collected through websites, applications, and SDKs.
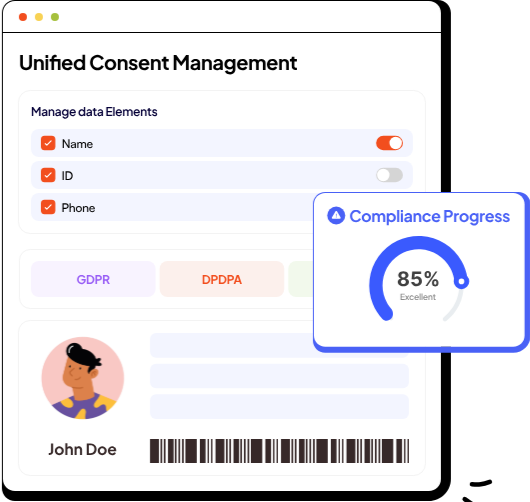
When someone withdraws consent, the update reaches downstream systems and website tags. A tamper-evident record shows when the change occurred.
Rights requests: Each request appears in a queue with its deadline, helping your DPO identify delays before time runs out.
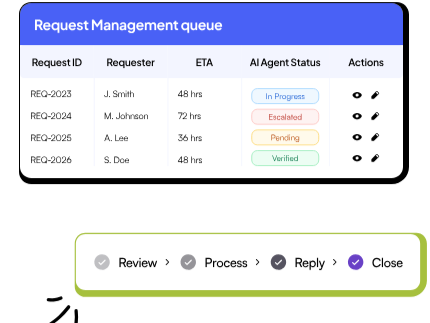
Redacto finds the requester’s data across your systems and redacts other people’s details before sending the response.
PIAs: When a new product or project starts, it completes a questionnaire and receives an AI risk score.
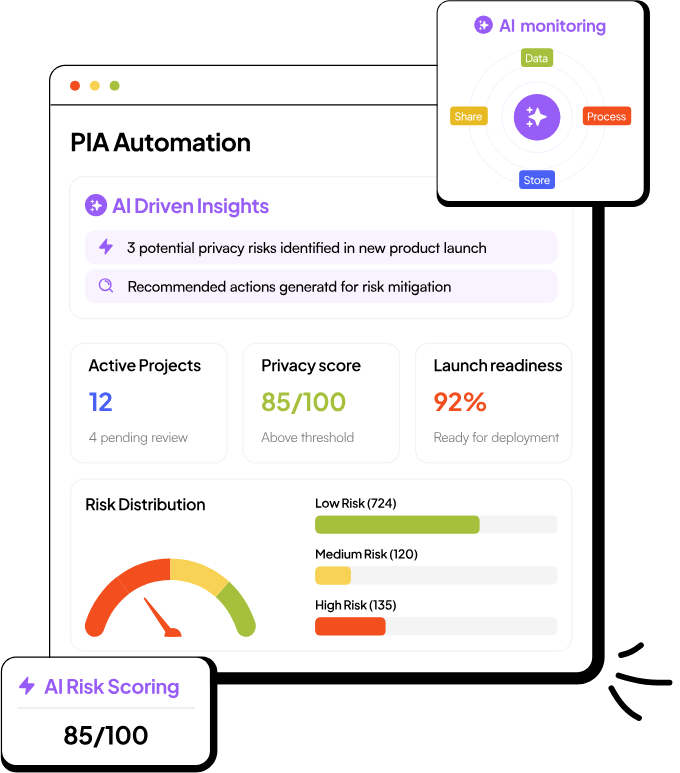
Your DPO reviews the identified risks and remediation report instead of building each assessment from scratch.
Vendors: Redacto sends questionnaires, scores vendors, and monitors them against agreed service levels.
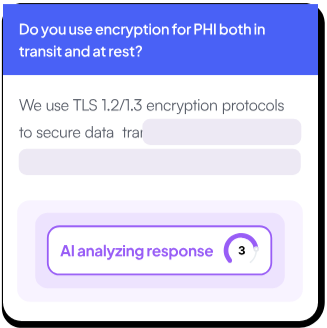
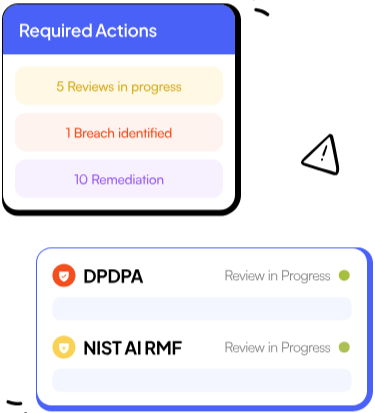
Reviews can use standards such as the NIST AI RMF. Your DPO receives an alert when a vendor’s risk changes.
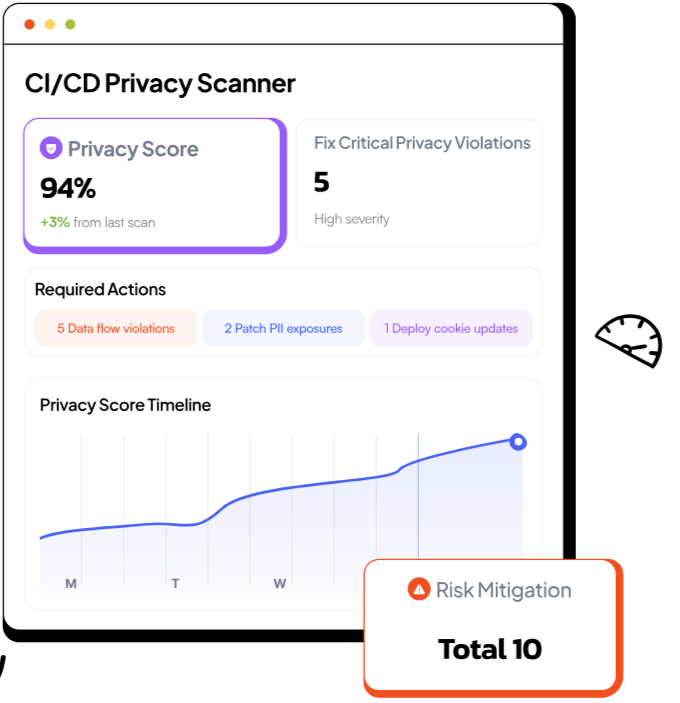
Code: The CI/CD scanner checks code, configuration files, and APIs for privacy issues before release, reducing the risk of your DPO reviewing a feature only after launch.
During a breach, notices stay on schedule
Section 8(6) requires notices to the Data Protection Board and every affected Data Principal. Redacto’s Breach Notification Engine includes:
- Playbooks for both notices
- Workflows for the immediate notice and 72-hour detailed report
- An evidence bundle covering the timeline, affected data, and containment work
If the breach begins with a vendor, the vendor incident response feature adds the vendor’s details to the same record. Your DPO and CISO can then work from one version of events.
Every quarter: what goes to your board
If you are a Significant Data Fiduciary, your DPO reports to the board. The board will expect more than a verbal update.
Redacto’s audit tools run DPDPA compliance audits using templates, automatically collect evidence, and produce scheduled reports with dashboards.
The Trust Center stores your policies, certifications, and evidence in one place.
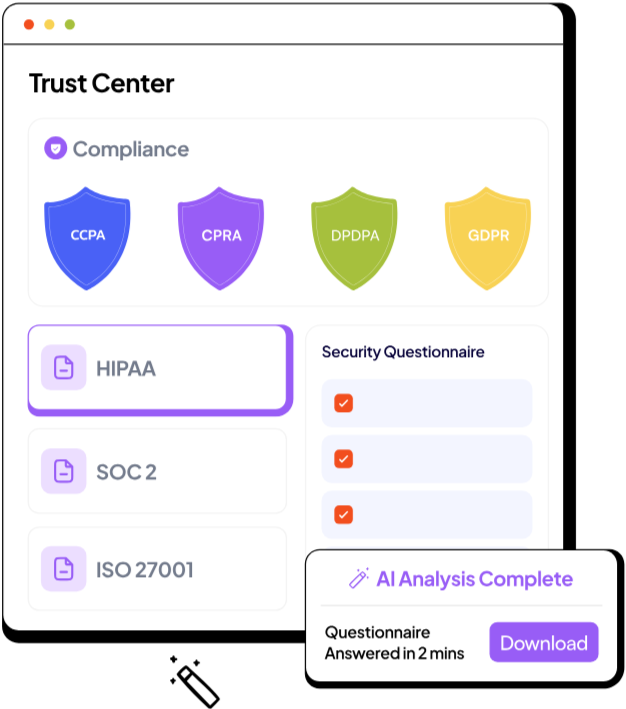
It also drafts responses to customer security questionnaires, reducing your DPO's manual workload.
Fitting Redacto around your DPO
Redacto connects through more than 7,000 prebuilt integrations, APIs, and webhooks. You can deploy it on your own servers, in a private cloud,d or as SaaS.
If you use an outsourced DPO, you can give them platform access instead of sending copies of files.
Conclusion: Which is the best DPO-as-a-service firm
The best firm is the one that will confirm in writing who your DPO is and what that person will do when a rights request or breach arrives.
Each provider above handles parts of the role well, but each also leaves questions unanswered. Take those questions into your first call and make sure the answers appear in the contract before signing.
Whichever firm you choose, your DPO will still need evidence of the work. That includes consent records, request logs, PIA decisions, and breach notices that your board or the Data Protection Board can review.
Redacto keeps those records in one place for any DPO, whether internal or outsourced. Book a Redacto demo to see how it can support your DPO before the 13 May 2027 deadline.