7 best data protection law firms in India before the DPDP deadline


If you’re wondering whether a DPDP privacy policy template can replace a law firm, consider what a template cannot do. It cannot compare your consent notice with the data your product actually collects.
It cannot draft DPAs that set vendor breach timelines and audit rights. And if something goes wrong, it cannot decide whether you must report the breach or represent you before the Data Protection Board.
The stakes are high. Penalties can reach ₹250 crore for failing to protect personal data and ₹200 crore for failing to report a breach. Full compliance is due by 13 May 2027.
Once you decide you need legal support, choosing the right firm becomes harder. Every firm presents itself well, so I compared them using four questions you might ask in your first meeting.
- Is their DPDP work current? The DPDP Rules were notified in November 2025, but some firms still publish material that predates the Act.
- How far do they go beyond drafting? A policy only helps if your systems follow it. I checked which firms also map data, conduct DPIAs, or audit the outcome.
- Who handles your breaches and disputes? Not every firm that advises on breach notices will represent you before the Data Protection Board or in court.
- What backs their claims? Independent rankings and named lawyers carry more weight than a firm describing itself as “leading.”
Below, I assess seven firms using those questions and point out the gaps in their published information. Further down, I explain how to make sure their advice is carried out in practice.
Best data protection law firms at a glance
- AMLEGALS: DPAs and transfer advice across India, the Gulf and Singapore.
- Spice Route Legal: Tier 1-ranked team for health data and tech products.
- Argus Partners: Court-tested counsel for social media and online platforms.
- Ahlawat & Associates: Data mapping through audit, including parental consent for young users.
- SMV Chambers: Privacy audits followed by fixes alongside your in-house team.
- Khaitan: Privacy support backed by employment, competition, and white-collar crime specialists.
- Fidus Law Chambers: RBI and DPDP consent requirements for fintech and health-tech apps.
How I evaluated each data protection law firm
I assessed all seven firms based on what they publish about their data practices. I used six questions that help show whether a firm can support you before the May 2027 deadline. Where a firm left something unclear, I included what to ask.
1. Is the advice current?
The DPDP Rules were notified in November 2025. If a firm still refers to the Data Protection Bill or “upcoming” rules, I flagged it so you can ask for recent examples.
2. How far does the firm go beyond drafting?
Some firms only write and review documents. Others map data, conduct DPIAs, coordinate technical changes or audit the results. I noted where each firm’s work appears to stop.
3. What happens during a breach?
I checked whether the firm helps decide whether notification is required, prepares Section 8(6) notices, and manages communication with staff, investors, and the press.
4. Can they defend you?
I looked for court, dispute, and Data Protection Board representation, not only compliance advice.
5. Do they understand your sector?
Health data, fintech consent, children’s data in gaming, and platform liability each bring different risks. I matched firms with the sectors where they show relevant experience.
6. What supports their claims?
I weighted independent rankings, named lawyers, and client work more than claims of being “top” or “leading.” I also checked how recent the rankings were.
The 7 Best Data Protection Law Firms in 2026
1. AMLEGALS
If you want a privacy lawyer who also works on AI law, AMLEGALS founder Anandaday Mishra has 27 years of legal experience. He also teaches data privacy and AI law in an executive program at Dhirubhai Ambani University’s School of Law. The firm operates from eight Indian cities, including Mumbai, Delhi, Bengaluru, and Hyderabad.
Its services focus on legal advice and drafting.
- Advice on DPDP requirements for consent, storage and transfers
- Privacy policies
- Data processing agreements for multiple jurisdictions
- Reviews of your DPIAs
- Advice for your Data Fiduciary team and DPO
- Staff training and breach management support
The firm reviews your DPIA rather than conducting it and advises your DPO instead of acting as one. Your team remains responsible for implementing the changes.
Why AMLEGALS is better for data protection contracts across several countries
Vendor and processor contracts turn your data obligations into enforceable terms. AMLEGALS drafts and reviews data processing agreements that cover:
- Processing scope and security requirements
- Sub-processor approval and audit rights
- Breach notification timelines
- Data return or deletion when the contract ends
This becomes more useful when your data moves through the Gulf or Singapore. The firm covers the UAE and Saudi PDPL and Singapore’s PDPA, alongside the DPDP Act, GDPR, and CCPA. One team can therefore draft contracts for all these markets.
Pros
- Founder with 27 years of experience who teaches AI law.
- Drafts DPAs for several jurisdictions.
- Covers UAE and Saudi PDPL alongside the DPDP Act.
- Operates from eight Indian cities.
Cons
- Advises and drafts while your team handles implementation.
- Its Vibe Data Privacy offering is not clearly explained.
- Some published DPDP guidance predates the notified Rules.
Best for
You have vendors or customers across India, the Gulf, Singapore or the EU and need one team for data processing agreements and transfer advice. It may also suit businesses adding AI features that need support covering the EU AI Act and privacy law.
2. Spice Route Legal
Legal 500, Chambers and Partners, Asialaw and Indian Business Law Journal rank Spice Route Legal’s data practice as Tier 1. Global Data Review also includes it among the world’s top 100 data practices.
The team handles disputes and advisory work, so the lawyers drafting your policies can also support you if a dispute follows.
Its day-to-day services include:
- Privacy policies and data processing agreements
- DPDP Act compliance advice
- Privacy built into products during the design stage
- Planning for data localization and residency requirements
The team has also worked across 50 jurisdictions, covering laws such as GDPR, CCPA, Nigeria’s data protection regulation, and Japan’s APPI.
I would raise two gaps early.
- Breach response is not listed as a service. Ask whether the team handles Section 8(6) notices to the Data Protection Board and affected Data Principals.
- It states sector experience covers technology, energy, mobility, and healthcare. If you work in BFSI or retail, ask for comparable examples.
Why Spice Route Legal is better for health data and tech products
Health data faces strict controls over where and how it can move. The team has advised on:
- Cross-border transfers and use of genomic data for pharmaceutical R&D
- Use of health data in COVID-19 vaccine development
- Localization of sensitive health data belonging to Indian citizens
Its data team also works with a life sciences practice that holds its own Tier 1 ranking.
For technology products, the team builds privacy into product design and has done this work for Big Tech platforms. If your product collects data at scale, you receive advice before launch instead of adding a policy afterward.
Pros
- Tier 1-ranked by Legal 500, Chambers and Asialaw.
- Handles data disputes alongside advisory work.
- Has advised on cross-border genomic data for pharmaceutical R&D.
- Has experience across 50 jurisdictions.
Cons
- Breach response is not listed among its services.
- Stated sector depth focuses on technology, energy, and healthcare.
- No lead lawyers are named.
Best for
You build technology products or handle health data, especially data moving across borders. You want a highly ranked team that can build privacy into your product and represent you if a dispute follows.
3. Argus Partners
At Argus Partners, data privacy forms part of a wider technology practice covering deals, regulation and court cases. Its lawyers are based in New Delhi, Mumbai and Bangalore. Its advisory services include:
- Advice on technology regulations, intermediary rules and cross-border data transfers
- Reviews of legal, regulatory and contractual risks when investing in or acquiring technology companies
- Support with outsourcing, technology transfer and licensing agreements for vendors and customers
- Compliance advice for social media companies covering online content, e-commerce, data privacy and cybersecurity
Check two points before hiring the firm.
- Ask for recent work under the DPDP Act and Rules. Its published privacy material still refers to the Data Protection Bill and the 2019 draft.
- Ask whether it runs compliance programs. It does not list consent, rights requests, or breach notices, suggesting the practice may focus more on deals and disputes.
Why Argus Partners is better for tech platforms that may end up in court
If your platform hosts user content, data and content issues can lead to legal action. Argus Partners has represented major social media companies before the Supreme Court, several High Courts and lower courts in:
- Defamation and intellectual property cases
- Public interest cases seeking regulation of social media and OTT platforms
The same lawyers advise on intermediary duties and online content laws. They also help shape legal strategy before a case is filed, allowing the team that develops your compliance position to defend it in court.
Pros
- Has represented social media companies before the Supreme Court.
- Covers intermediary rules and online content laws.
- Reviews data risks in technology investments and acquisitions.
- Drafts outsourcing, technology transfer, and licensing contracts.
Cons
- Published privacy work predates the DPDP Act.
- Consent, rights requests, and breach notices are not listed.
- No data privacy lawyers are named.
Best for
You operate a social media, OTT, or e-commerce platform, or you are investing in or acquiring a technology company. You need lawyers who can handle data privacy alongside intermediary rules, deals, and court cases.
4. Ahlawat & Associates
Ahlawat & Associates offers a six-step DPDP compliance process. It begins by mapping your data and ends with an audit of each business unit. Between those stages, the team reviews your current setup, plans the changes, and drafts the required documents. It also advises on technical implementation and can work with your service providers.
The process covers:
- Consent notices, privacy policies and cookie disclosures checked against your backend systems
- Retention schedules with automated deletion triggers
- Staff data policies covering background checks and workplace monitoring
- DPAs, vendor contracts and SaaS agreements with liability and indemnity terms
- Representation in complaints before the Data Protection Board and courts
The team works from Delhi, Chandigarh, and Mumbai. Confirm two points in the proposal.
- Foreign law coverage. Its published work focuses on the DPDP Act. Ask what is included if you also fall under GDPR or other laws.
- Audit frequency. Ask whether the audit is a one-time final review or runs regularly.
Why Ahlawat & Associates is better for gaming and consumer apps with young users
The DPDP Act has separate requirements for children’s data. You need verifiable parental consent before processing a child’s data, and restrictions apply to targeted advertising. Breaches of these duties can lead to penalties of up to ₹200 crore.
The team designs parental consent systems that meet the law. Its work includes gaming and social media, where large numbers of young users increase the risk.
If a breach occurs, the team handles more than the filing. It advises on:
- Whether notification is required and when
- Your legal exposure
- Communication with the regulator, staff and investors
Pros
- Uses a six-step process that ends with an audit.
- Designs verifiable parental consent systems.
- Handles breach fallout, including investor communication.
- Represents clients before the Data Protection Board.
Cons
- Foreign privacy law work is not described.
- Audit frequency is not stated.
- No lead lawyers are named.
Best for
You run a gaming, social media, e-commerce, or health-tech platform under the DPDP Act, particularly one with young users. You want one firm to guide you from data mapping through audit.
5. Khaitan
You would be hiring a team that helped shape India’s first draft data protection bill. Khaitan’s privacy lawyers took part in consultations with the Justice Srikrishna Committee, and the Government of India directly requested their input on the Personal Data Protection Bill. That background can help when the law does not provide a clear answer.
The practice covers:
- Compliance advice, policies and DPAs
- Cross-border transfers and government requests for data access
- Data security and breach notification
- Data issues in transactions
- AI, cloud computing, blockchain and IoT
- Defense in investigations and proceedings involving privacy or security failures
I would want two questions answered first.
- What recent DPDP Act work can the firm show? Its published practice material refers to the PDP Bill and 2021 rankings, with nothing on the DPDP Act, 2023, or the 2025 Rules.
- Who will handle your matter? The client list focuses on Fortune 100 and 500 companies. Startups and mid-sized businesses should ask who will manage the day-to-day work.
Why Khaitan is better for data issues that cross into other areas of law
A breach or data dispute can involve employment, competition, tax or criminal law. Khaitan’s privacy team can bring in the firm’s specialists in these areas, along with its TMT, intellectual property and dispute resolution teams. You do not need to brief a new firm when the issue expands.
Its sector experience includes BFSI, telecom, telemedicine, edtech, pharmaceuticals and manufacturing.
Pros
- The privacy team is supported by competition, employment, and white-collar crime specialists.
- Defends clients in privacy investigations and proceedings.
- Advises on government data-access requests.
- Works with Fortune 100 and 500 companies.
Cons
- Published practice material predates the DPDP Act.
- Its cited rankings are from 2021.
- Its client list leans towards large multinational companies.
Best for
You are a large company or multinational operating in India, and a data issue could involve regulators, employees, or criminal exposure. You want one firm to handle privacy and the related legal issues.
6. Fidus Law Chambers
Fidus Law Chambers conducts DPIAs instead of only reviewing assessments your team prepares. It also designs notice and consent processes, including opt-in and opt-out flows. The team then builds privacy requirements into vendor management, product launches and marketing.
Its other services include:
- Internal policies for data retention, grievance handling and security
- Advice on lawful grounds for data collection and user rights
- Staff training and sector-specific controls
- Cross-border transfers under GDPR, the UK Data Protection Act, Singapore’s PDPA and US state laws
Check two points before shortlisting the firm.
- Ask for references from your sector. It publishes no rankings, named lawyers, or client examples, so you will need another way to confirm its experience.
- Confirm whether it handles disputes. The team communicates with the Data Protection Board after a breach, but it does not list complaint defense or court cases.
Why Fidus Law Chambers is better for fintech and health-tech apps
A fintech app must follow RBI requirements and the DPDP Act at the same time. Fidus advises on RBI data localization and consent processes for account aggregators and UPI apps, where consent and data flows are tightly controlled.
For health-tech companies, the team covers health data rules, telemedicine ethics, and electronic health records. Its edtech and e-commerce work includes consent verification for minors and rules on profiling and targeted advertising.
If a breach happens, the team:
- Notifies regulators and affected users
- Coordinates forensic investigations with cybersecurity experts
- Manages communication with the Data Protection Board and the press
Pros
- Conducts DPIAs instead of only reviewing them.
- Advises on account aggregator and UPI consent processes.
- Breach support includes forensic coordination and PR.
- Covers GDPR, UK, Singapore, and US state laws for transfers.
Cons
- No rankings, named lawyers, or client examples are published.
- Dispute and court work is not listed.
Best for
You operate a fintech, health-tech, or edtech app and want lawyers who can build DPDP and sector requirements into the product, from consent flows to DPIAs.
7. SMV Chambers
Start here if you do not yet know where your privacy gaps are. SMV Chambers conducts full privacy audits and readiness assessments. It then works with your legal, IT, and compliance teams to address what the audit finds.
Its services include:
- Consent management and rights requests
- Staff data handling rules and internal privacy governance
- Privacy policies, DPAs and privacy terms for B2B and B2C customers
- Vendor risk assessments and cross-border transfers under the DPDP Act, GDPR and HIPAA
- Breach notification advice and incident response plans
- Privacy terms for mergers, outsourcing and technology contracts
Two questions remain open.
- What is the firm’s track record? SMV describes itself as a top firm but publishes no rankings, named lawyers or client examples. Ask for references.
- What does “rapid response” mean during a breach? Get response times in writing and confirm whether the firm handles Section 8(6) notices to the Data Protection Board and affected Data Principals.
Why SMV Chambers is better for starting with a full privacy audit
If you do not know what personal data you hold or where it moves, writing policies first means working without a clear picture. SMV begins by auditing your data practices, policies, controls, and contracts. It then creates handling rules your teams can follow.
Its lawyers work alongside your staff and IT security professionals rather than taking over the process. This suits businesses with an existing legal or compliance function that needs outside support.
Pros
- Starts with a full privacy audit.
- Works alongside your legal and IT teams.
- Drafts privacy terms for B2B and B2C customers.
- Covers privacy in mergers and outsourcing contracts.
Cons
- No rankings, named lawyers, or client examples are published.
- Breach response times are not defined.
- Court and dispute representation is not listed.
Best for
You have an in-house legal or IT team but lack a clear view of your privacy gaps. You want outside counsel to conduct an audit and then work with your team on the fixes. It also suits businesses serving companies and consumers that need privacy terms for both.
Where Redacto fits: your lawyer advises, your team needs proof
Your lawyers explain what the DPDP Act requires. Redacto gives your team a way to carry out that advice every day and keep evidence.
It was built for the DPDP Act, not adapted from a GDPR tool, and BFSI and fintech companies already use it in production.
Start with what you actually hold
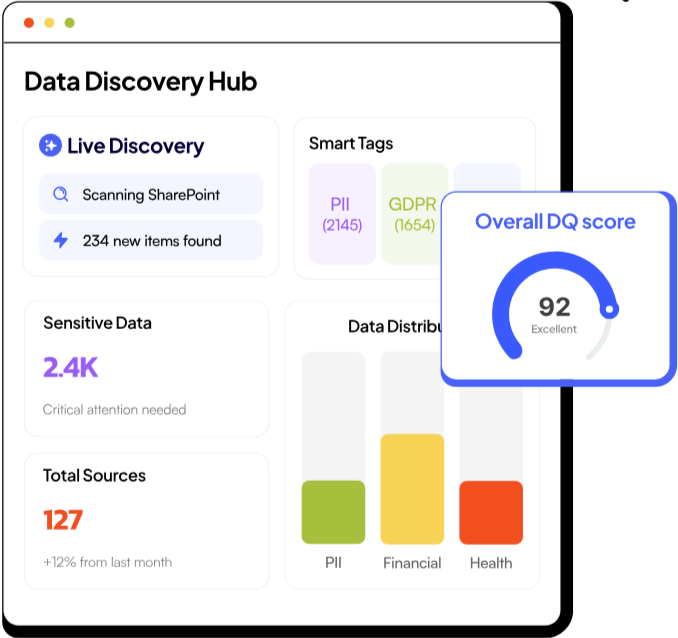
Privacy advice begins with one question. What personal data do you hold, and where does it go? Redacto answers this from your systems instead of relying on a spreadsheet. It:
- Scans databases, apps, and cloud storage to list every data source
- Tags each element as personal, health, or financial data, along with custom tags
- Traces how data moves from its source to its destination
- Rescans changed sources and updates the tags
Your lawyer can then advise based on the data you actually hold, not what your teams remember.
How the work splits after your lawyer advises
Consent: Your lawyer drafts the notice. Redacto manages notice versions and collects consent through the web, apps, and SDKs for iOS, Android, and React.
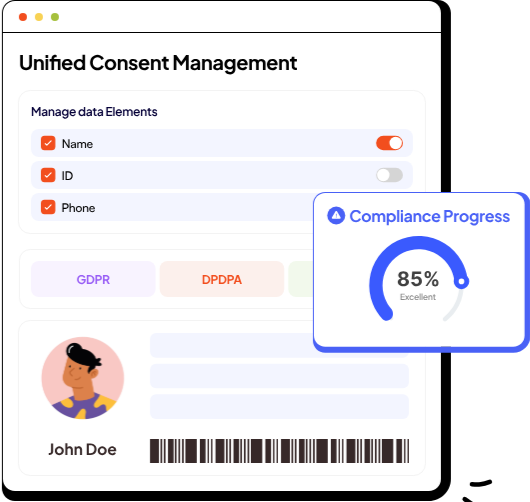
It connects opt-outs with website tags and cookies and sends withdrawals to downstream systems.
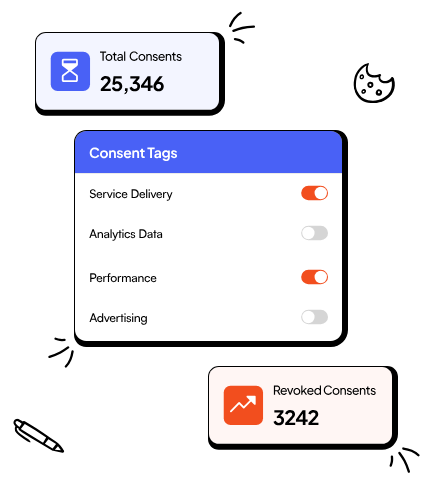
Users manage their choices through a branded privacy center, while every consent is stored in a tamper-evident record.
Rights requests: Your lawyer defines your duties. Redacto searches databases, apps, and cloud storage, matches records to the request, and redacts other people’s data before release.
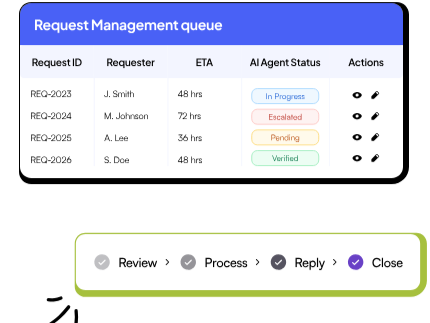
Requests move through review, processing, response, and closure in a queue with deadlines. The right teams are notified when a request arrives.
DPIAs: Your lawyer sets the approach. Redacto uses pre-built questionnaires with AI risk scoring, supports templates for areas such as healthcare and financial services, maps data flows, and reports findings with recommended fixes.
Vendors: Redacto sends vendor questionnaires, imports third-party risk assessments, scores and ranks vendors, and tracks them against agreed SLAs.
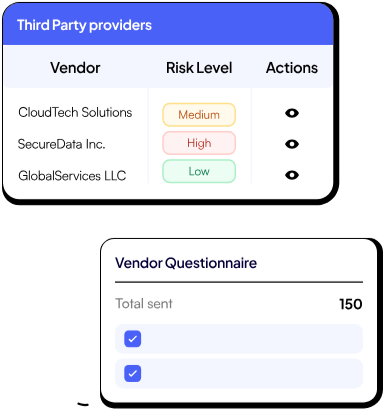
It alerts you when a vendor’s risk changes or a security incident occurs.
Breaches: Your lawyer writes the response plan. Redacto’s Breach Notification Engine runs it using playbooks for notices to the Data Protection Board and affected individuals.
It supports immediate notice and a 72-hour detailed report, and creates an evidence bundle covering timelines, data types, and containment steps.
Code: Lawyers do not review your code. Redacto’s CI/CD scanner checks code, configuration files, and APIs during development.
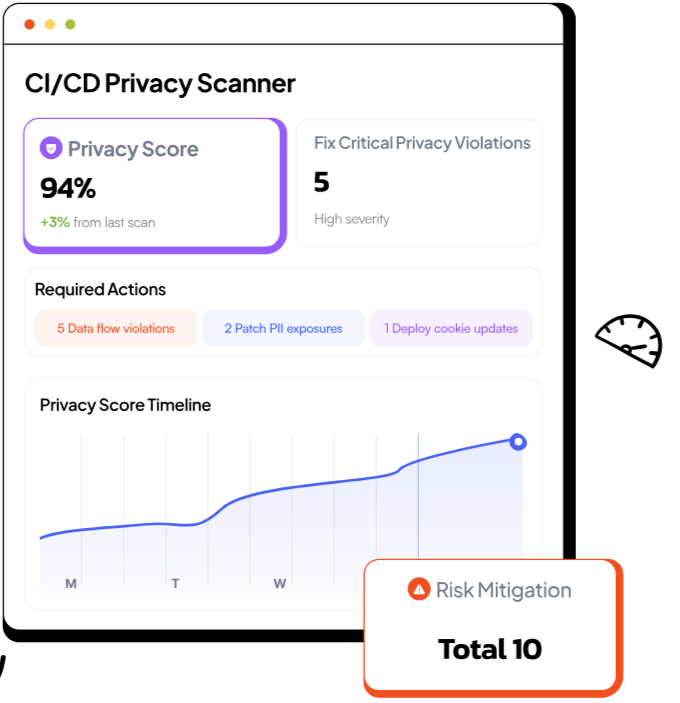
It flags missing consent systems, improper use of personal data, and unsafe data-sharing settings before release.
What your law firm gets to review
When your lawyers audit you, Redacto gives them records instead of a folder filled with policies:
- DPDPA compliance audit templates
- Evidence gathered automatically
- Scheduled reports covering findings and compliance status
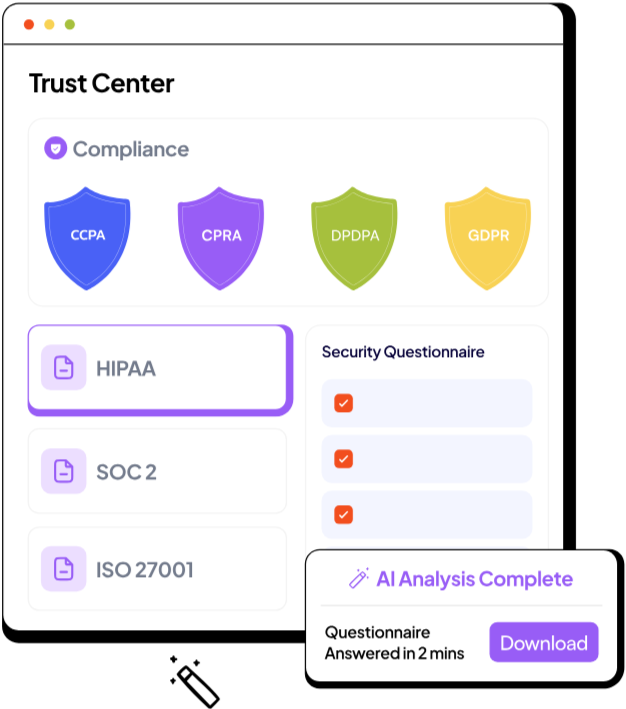
The Trust Center stores your policies, certifications, and evidence in one place and drafts responses to customer security questionnaires.
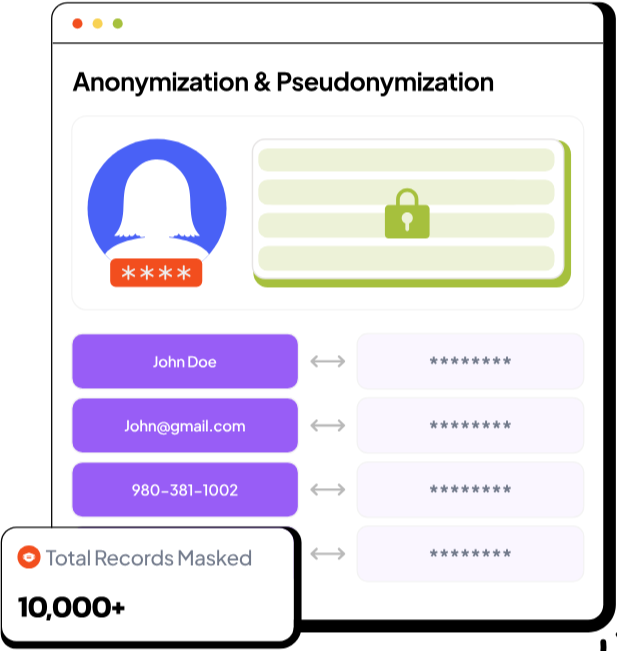
Anonymization, pseudonymization, and tokenization also let teams test and analyze data without revealing real identities.
Fitting it into your stack
Redacto connects through more than 7,000 pre-built integrations, APIs, and webhooks. You can run it on your own servers, in a private cloud, or as SaaS. Teams whose data cannot leave their infrastructure can keep it in-house.
Conclusion: Which data protection law firm is best?
Start with your biggest risk, not the biggest name. If a breach could expose health records, a lawsuit could affect your platform, or many of your users are children, a firm with direct experience in that area may serve you better than one with a longer client list.
Shortlist two firms and send them the four questions from the beginning of this guide. Ask each firm for an example of recent work under the DPDP Act and the 2025 Rules. Their answers will tell you more than any ranking.
Whichever firm you choose, its advice will reach you as notices, DPAs, DPIA methods and breach plans.
Redacto gives your teams a place to run that advice through consent records, rights requests, vendor reviews and breach notices while keeping evidence your lawyers can audit.
Book a Redacto demo to see how your firm’s advice would work inside the platform before full compliance becomes due on 13 May 2027.